Skip to content
Nodal Technologies

Resources

New releases from the Nodal team land here first: case studies, white papers, interactive explainers, videos and writing. Filter by type, or search.
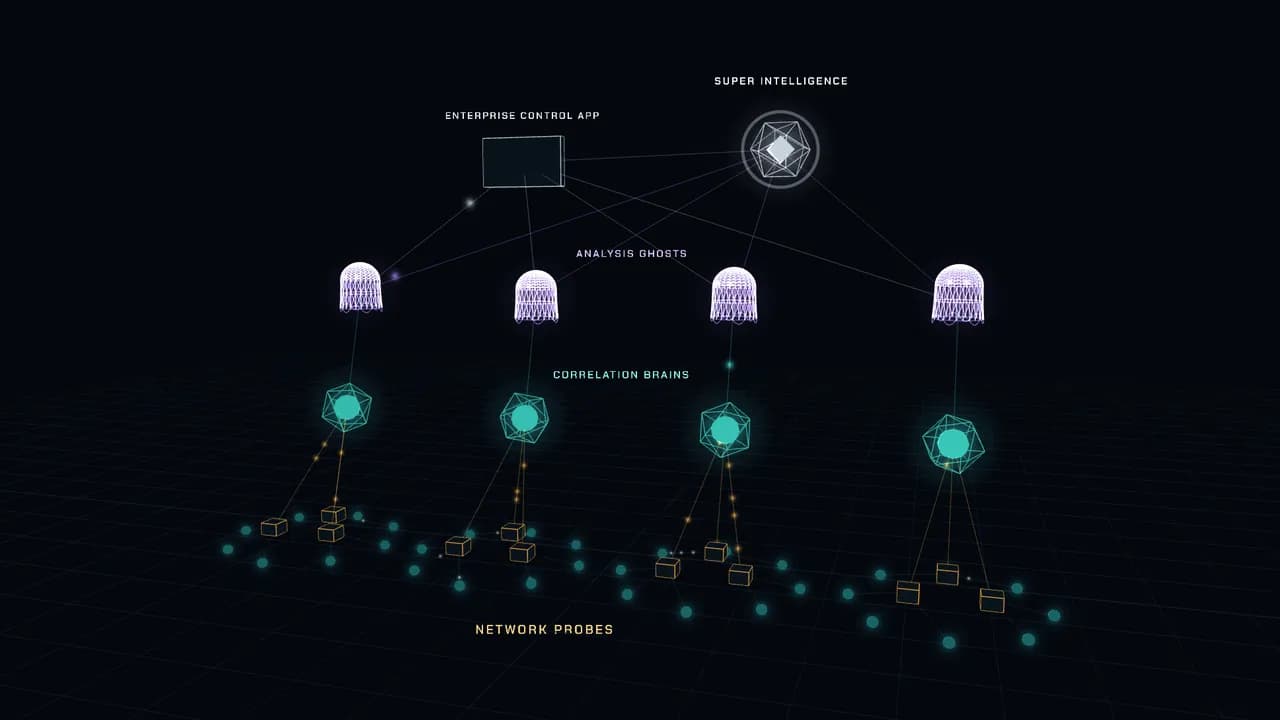
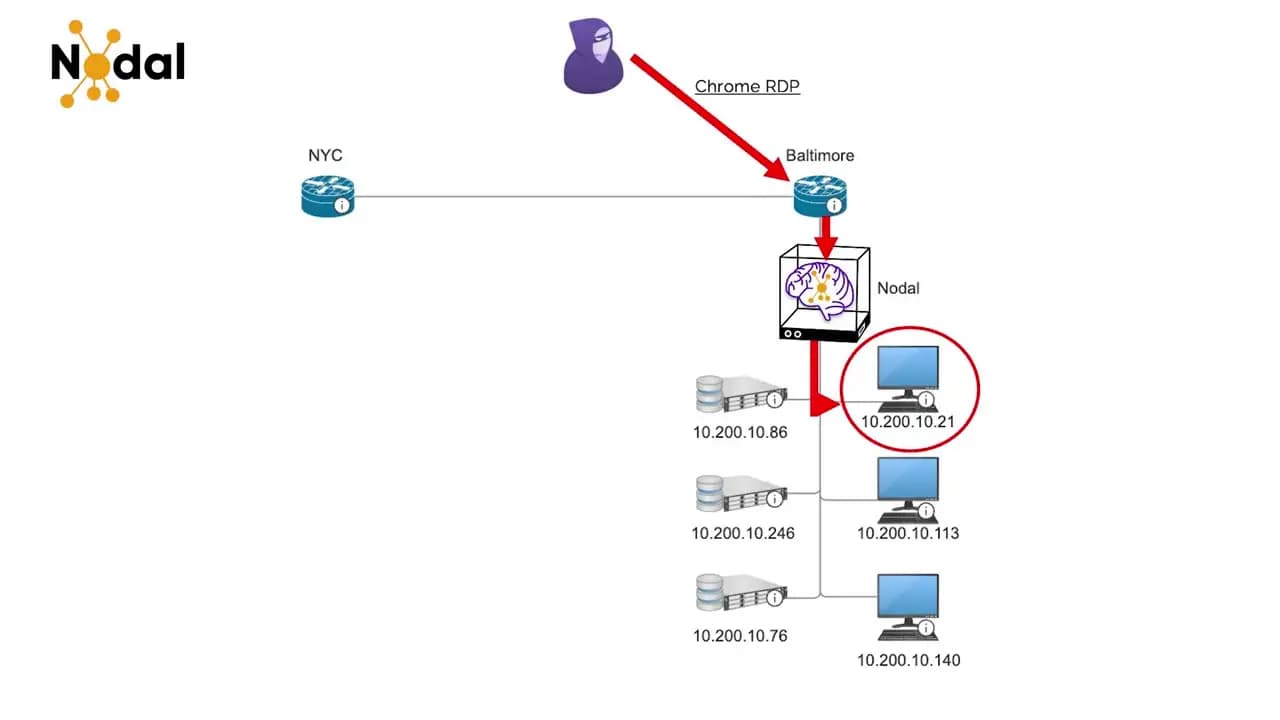
  • Video4:52A campaign, disrupted: the full walkthrough4:52 · 8 October 2026One stolen account becomes a path into the network. Watch the chain assemble across routers and hosts, and watch the command-and-control channel get cut while every device stays online.
  • Case study

    How a four-hop campaign was cut in a resort network

    17 pages/18 min read

    What is inside

    1. 01The environment, and why it was a soft target
    2. 02Day one: what the existing stack had already seen
    3. 03Reconstructing the path across four hops
    4. 04The disruption, and what stayed online
    5. 05What we would tell the next team in this position
    Every hop in the chain used the systems' own tools. There was no malware to find, which is why nothing had been found.

    Your copy opens as soon as you send this.

    Request: How a four-hop campaign was cut in a resort network

    By requesting this you agree that Nodal Technologies may contact you about it and store the details above.

  • White paper

    A supply-chain intrusion inside a law firm, caught by behaviour

    18 pages/22 min read

    What is inside

    1. 01Why a legal practice is a high-value, low-friction target
    2. 02The trusted update: how signed software becomes the entry point
    3. 03Eleven days of living off the land, stage by stage
    4. 04The forty-seven signals, and why every one was judged correctly
    5. 05Reconstruction: linking events by behaviour rather than by source
    6. 06Disrupting at the edge without taking a single matter offline
    7. 07What a firm without a security team can reasonably do
    The intrusion arrived through software the firm had been told to trust, signed by a vendor they had paid to trust it.

    Your copy opens as soon as you send this.

    Request: A supply-chain intrusion inside a law firm, caught by behaviour

    By requesting this you agree that Nodal Technologies may contact you about it and store the details above.

  • WalkthroughWatch a campaign get caughtInteractiveOne intrusion, traced from a stolen credential to a severed command-and-control channel. Every technique real, none of it malware, and the reason a conventional stack stays quiet throughout.
  • Video5:13 Beating the 22-Second Clock: Catching Attackers After the Breach5:13 · 8 October 2026Attackers now hand off access to a compromised network in a median of 22 seconds. Once inside, they move between systems faster than most security teams can respond. How Nodal can detect and contain adversaries as the attack unfolds.
  • BlogThe hop that cannot run an agent24 June 2026 · 3 min readPrinters, controllers, imaging systems and legacy appliances carry real traffic and take no security software. In most environments they are the middle of the attack chain and the blindest spot in the record.

See it work

When you're ready to see campaign detection live.

Thirty minutes with a Nodal engineer: a real campaign detected, traced to its command-and-control and cut, on your questions rather than a script.